Summary
Firmware patches for the Edge Series hardware and virtual devices listed below are planned for release on December 3, 2026. These patches update the Linux kernel to fix CVE-2026-98432, a use-after-free vulnerability in the IPv4 TCP stack (ireq_opt).
The IPS rules and applicable VDS patterns listed under Threat Coverage are available now. Customers can update their patterns and enable self-protection where applicable before installing the firmware patch.
Firmware Patches and System Upgrades
Edge Series Devices
| Product | Planned firmware patch |
|---|---|
| EdgeIPS Pro and Virtual EdgeIPS Pro | Firmware 2.3 patch |
| EdgeIPS 103, EdgeIPS 102, and EdgeIPS LE | Firmware 2.3 patch |
| EdgeFire IEF 1012 and EdgeFire IEF 1014 | Firmware 2.2 patch |
No patch is currently planned for firmware 1.x. Customers running firmware 1.x should upgrade to the latest v2 firmware for their device.
EdgeOne
| Current version | Upgrade path |
|---|---|
| EdgeOne 2.4–2.7 |
Upgrade to EdgeOne 2.7.12 or later using the applicable image (egone.fw, egone.cms.v2, or egone.cms.v13). |
| EdgeOne 2.0–2.3 |
Upgrade directly to EdgeOne 2.7.12 using the upgrade image on the MyTXOne Portal. |
Mitigation Before Upgrading
Edge Series Devices
- Update to the latest IPS pattern.
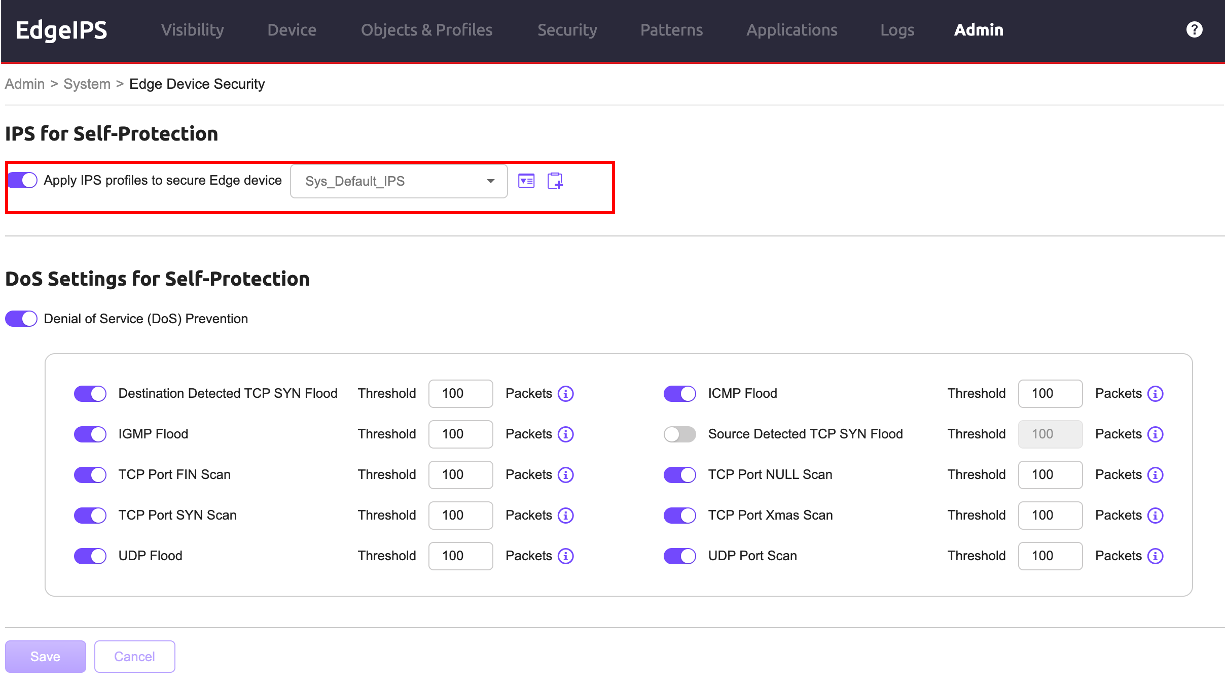
- In the device console, go to Admin → System → Edge Device Security.
- Under IPS for Self-Protection, enable Apply IPS profiles to secure Edge device.
- Select the IPS profile and click Save.
EdgeOne, ODC, and TPS
| Product | Recommended action |
|---|---|
| EdgeOne | Update to self-protection pattern TXv2_SDP_261030_1 or later. |
| ODC | Upgrade to ODC 1.5 or later and apply the latest self-protection pattern (SDP_261030_15 for ODC-VA). Alternatively, migrate to EdgeOne 2.7.12 or later and enable self-protection with pattern TXv2_SDP_261030_1. |
| TPS | Apply self-protection pattern SDP_261030_15. |
Threat Coverage
Check Pattern Versions on the MyTXOne Portal for the latest IPS and VDS patterns.
| Threat | Detection coverage | Recommended action |
|---|---|---|
| PHP2Shell (CVE-2026-109618) |
Five IPS rules and a VDS pattern | Update to the latest IPS and VDS patterns. This coverage is supported across the Edge product family and requires only a pattern update. |
| Node2Shell (Google Brotli, CVE-2026-111497) |
Two IPS rules and a VDS pattern | Update to the latest IPS and VDS patterns. No additional product action is required for this threat. |
| PXE (CVE-2026-97631) |
Four IPS rules. No VDS pattern is available for this threat. | Update to the latest IPS pattern to protect exposed assets behind EdgeIPS or EdgeFire. EdgeIPS and EdgeFire hardware appliances are unaffected by this vulnerability. |
| Linux Kernel TCP (CVE-2026-98432) |
One IPS rule and a VDS pattern | Update the patterns and follow the steps under Mitigation Before Upgrading. Apply the applicable firmware patch or system upgrade when it becomes available. |
IPS Rule Details
| Threat | IPS rule IDs | Rule name |
|---|---|---|
| PHP2Shell | 1239165, 1239169 |
Zend Memory Manager Uninitialized Memory -1 |
| PHP2Shell | 1239168, 1239172 |
Zend Memory Manager Uninitialized Memory -2 |
| PHP2Shell | 1239176 | Suspicious Large Serialized Array Declaration (generic behavior rule) |
| Node2Shell | 1239180, 1239190 |
Google Brotli Unchecked Return Value -1 / -2 |
| PXE | 1239200 – 1239203 | ICMP Specific ICMP Type with Large Size Payload -1 to -4 |
| Linux Kernel TCP | 1239204 | EXPLOIT Linux Kernel IPv4 TCP ireq_opt Use After Free |
Downloads
Please refer to the Download Center Knowledge Base for the latest firmware, pattern, and documents.